CSK 2026 [Conference] The AX Era: What National AI Security Strategy Is Needed?
At CSK 2026, the session “National AI Security Strategies Needed in the AX Era” discussed national-level security strategies for addressing increasingly sophisticated cyber threats as AI transformation accelerates.
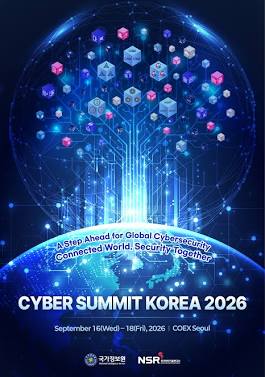
Cyber Summit Korea (CSK) 2026. (Source: CSK 2026 Cyber Summit Korea website)
CSK 2026 Session A-2: The AX Era: What National AI Security Strategy Is Needed?
As artificial intelligence (AI) is applied rapidly across work and entire industries, the standards for cybersecurity are changing along with it.
Where security in the past focused on protecting IT infrastructure like computers, networks, and servers, it is now expanding into a situation where AI models and data, AI agents, and even automated decision-making processes must be protected too.
Held against this backdrop, Cyber Summit Korea (CSK) 2026 featured a session discussing what security strategy is needed at the national level in the era of AI transformation, or AX (AI Transformation).
Among these, Session A-2, "The AX Era: What National AI Security Strategy Is Needed?" looked at the cyber threats that shift as AI adoption expands, and the national-level response system for them.
1. Why did CSK 2026 discuss 'national AI security strategy'?
CSK 2026 was a global cybersecurity event jointly hosted by the National Intelligence Service and the National Security Research Institute, held at COEX Seoul in September 2026.
This year's theme was "A Step Ahead for Global Cybersecurity: Connected World, Security Together."
According to the official program, Session A-2 ran from 3:30 to 5:00 p.m. on September 17, chaired by Lee Won-tae, chair of the security special committee of the National AI Strategy Committee.
The panel included Professor Kim Chang-hoon of Daegu University, CEO Choi Young-chul of SGA Solutions, Country Manager Park Sang-kyu of Palo Alto Networks Korea, and CISO Hong Kwan-hee of LG Uplus.
The organizers described the session's core discussion as responding to new threats that come with the convenience AI brings, and exploring an AI security strategy that secures technological sovereignty and supports the transition to AX.
In other words, the key question wasn't just how quickly to adopt AI, but also
"What security foundation needs to be in place first in order to use AI safely?"
2. In the AX era, the very speed of attack and defense changes
One of AI's biggest characteristics is that it can rapidly automate analysis and tasks that used to be done by people.
This trait is an advantage for defense, but it can be exploited on the attack side too.
For example, AI can be used to automate analyzing large volumes of data, reviewing software code, and finding potential vulnerabilities.
One example cited at CSK 2026 that illustrates this concern was the use of high-performance frontier AI in cybersecurity.
Country Manager Park Sang-kyu of Palo Alto Networks Korea shared, during the session, his company's experience using high-performance AI to check for vulnerabilities as part of 'Project Glasswing,' a cybersecurity collaboration project with Anthropic.
According to reports, he described a case where vulnerability-discovery work that had taken his engineers a long time produced similar results with AI in a very short amount of time.
What matters about this example isn't so much the performance of a particular AI model, but rather how significantly the level of automation and speed applied to cyberattack and defense can change.
3. AI is both a security 'tool' and a new attack surface
Using AI for security doesn't mean every problem gets solved.
That's because the AI system itself can become a new target for attack.
Breaking the components of an AI service down simply looks like this.
AI model → data → application → API → user → external system
The more AI connects to other services, the more area there is that needs to be protected.
In particular, in environments where AI agents connect to external services or work systems and carry out tasks on their own, it can become difficult to manage every risk with traditional, simple information-security methods alone.
Indeed, other sessions at CSK 2026 also covered major topics like the potential for autonomous attacks by high-performance AI, Agentic SOC, and vulnerability discovery using LLMs.
So AI security going forward is likely to expand beyond simply
"how to use AI safely"
to also cover
"how to manage the risks that can arise as AI interacts with other systems"
.
4. A discussion on the need for shared AI security standards
One point worth noting from this session is the problem of institutions and companies each managing security in their own different ways.
AI technology isn't used in just one industry.
Its use is increasing across many fields, including finance, telecommunications, manufacturing, healthcare, and public services.
But if AI security standards and management methods differ too much across organizations, responding jointly to national-level threats can become difficult.
On this issue, the CSK 2026 session reportedly presented the need for a national, common AI security framework that standardizes and integrates security controls scattered across multiple institutions.
Put simply,
this is an approach that moves away from every company protecting AI by its own separate standard, and instead sets up basic security standards that can be applied in common.
This matters not only for companies developing AI services, but also for public institutions and ordinary companies that use AI.
5. Connecting existing security systems with AI security
It's also not appropriate to treat AI security as an entirely separate, brand-new area.
That's because existing information-security systems and AI security need to be connected.
Companies and institutions today operate a range of security controls, including access control, account management, network security, personal data protection, and vulnerability management.
Once AI is introduced, the following elements need to be considered on top of that.
AI model security
The source, version, change history, and vulnerabilities of the AI models in use need to be managed.
Data security
It's necessary to manage whether personal data or a company's sensitive information is included in the data used during AI training or inference.
API and external service security
If AI uses external APIs or cloud services, that creates new connection points.
AI agent permission management
If AI goes beyond simply answering questions to modifying files or issuing commands to a system, it's necessary to clearly define what tasks it's allowed to perform.
Result verification
A system that lets humans verify code, commands, or analysis results generated by AI is also important.
Ultimately, AI security doesn't replace existing information-security systems — it needs to develop in the direction of incorporating AI as a new component within existing security.
6. Why zero trust is becoming important again
The session also touched on the need to upgrade security systems, including zero trust.
Put simply, zero trust is a security approach that means "don't automatically trust something just because it's inside the network".
This approach can become even more important in an AI environment.
For example, suppose an AI agent accesses a work system.
Instead of simply deciding "this AI is used by our company, so it's trusted,"
which AI is it?
who is it acting on behalf of?
what data is it accessing?
what tasks can it perform?
does it have permission to perform that task?
how will the results of its work be verified?
— a structure that continuously checks these kinds of things is needed.
Coverage from Boannews of the session's content also discussed the need for institutionalizing zero trust, automated defense systems, and real-time isolation systems.
7. Can AI security be solved with 'automation' alone?
Using AI for cybersecurity has the advantage of being able to automate security monitoring and response.
But automation brings another problem with it.
If AI makes a wrong judgment, that judgment can end up being carried out automatically.
For example, if a security AI mistakenly judges a normal system to be under attack and automatically blocks it, that can create a new problem of business disruption.
So the following structure matters in AI-based security.
Detection → analysis → judgment → execution → verification
Especially for critical systems, rather than leaving the entire process to AI, it may be necessary to add human approval or oversight depending on the level of risk.
Indeed, Country Manager Park Sang-kyu also mentioned the need for cost, resources, and expert involvement alongside using high-performance AI for vulnerability checks.
In other words, the future of AI security isn't simply about 'full automation' — it's connected to the question of how to properly divide roles between AI and security experts.
8. Technological sovereignty and the meaning of 'sovereign AI'
Another important keyword from this session was technological sovereignty.
As AI technology becomes deeply embedded in the core operations of nations and companies, dependence on AI models, data, and infrastructure can itself become an important security issue.
In particular, for AI used in critical national infrastructure or public services, the following questions become necessary.
Where was the AI model developed?
Where is the data processed?
Is important data transmitted externally?
How will you respond if the model or service goes down?
Who manages the AI system's security vulnerabilities?
Is dependence on a particular foreign technology too high?
This is why the concept of sovereign AI is also being discussed alongside these questions recently.
At CSK 2026, CEO Choi Young-chul of SGA Solutions reportedly also raised the need for sovereign AI and developing an independent foundation model, while discussing the importance of high-performance models for AI-based vulnerability checks and automated penetration testing.
That said, sovereign AI doesn't necessarily mean that every single AI technology must be developed in-house.
The core of it can be understood as the question of how to secure control over important data and AI systems.
9. National-level AI safety evaluation is expanding too
CSK 2026 also introduced developments related to national-level AI safety evaluation.
According to Yonhap News, the National Intelligence Service announced plans to expand safety evaluation — which had previously centered on large language models (LLMs) — to cover AI agents as well.
Plans to prepare related guidelines and security playbooks were also introduced, so that AI agent risks can be assessed and each institution can carry out its own security checks.
This shift is related to the fact that AI is evolving beyond simply answering questions into an agent form that actually carries out tasks.
As the scope of tasks AI can perform widens, it becomes necessary to evaluate not just the safety of the AI itself, but also what actions AI can actually take in a real environment.
10. The core elements that make up national AI security strategy
Bringing together what was discussed in the CSK 2026 session, a national security strategy for the AI era is difficult to build around a single technology alone.
The following elements need to work together.
① National, shared AI security standards
Institutions and companies need AI security standards and a framework they can commonly use.
② Securing AI security technology
Technology for protecting AI models and data, and for using AI to detect and respond to threats, need to be developed together.
③ Zero-trust-based access control
A system applying least privilege and continuous verification when AI and people access systems is important.
④ AI agent security
The actions and access permissions an AI agent can carry out need to be clearly managed.
⑤ Supply chain security
The entire supply chain that makes up an AI system — AI models, data, open-source software, external APIs, and more — needs to be managed.
⑥ Automated defense systems
AI should be used to speed up detection, analysis, and response, while proper verification procedures are put in place for important decisions.
⑦ Securing skilled personnel
Training experts who can understand both AI and cybersecurity together is needed.
⑧ Securing technological sovereignty
A national-level response capability for core AI technology, data, and security infrastructure needs to be secured.
11. AI-era security isn't about 'blocking AI'
There's a misunderstanding that can commonly arise about AI security.
That's the idea that not using AI would solve security problems.
But with AI already being used across a wide range of industries and services, simply restricting AI use alone is unlikely to solve the problem.
What actually matters more is identifying and controlling the risks that can arise while using AI.
While actively using AI,
who is connecting which AI, with what data, to which system, to perform what task
needs to be something you can check.
And when a problem occurs, a system for quickly detecting, isolating, and recovering from it is needed.
12. The question CSK 2026 Session A-2 poses
The question worth reflecting on from this session is a simple one.
"Are existing security methods alone enough in the AI era?"
If AI can analyze code, find vulnerabilities, process data, and connect to various systems faster than a person can, security needs to keep pace with that change too.
In particular, when the core systems of nations and companies get connected to AI, it's necessary to consider the possibility that a single vulnerability could spread to other systems.
So AI security is less a matter of adopting one particular security product, and more a comprehensive security issue that has to look at policy, institutions, technology, personnel, data, and the supply chain together.
13. Why AI security matters for ordinary users too
National-level AI security strategy isn't only a matter for governments or security companies.
The generative AI services individuals use are connected to AI security too.
For example, new security risks can arise if you enter a company's internal documents into an external AI service without any review, run program code generated by AI without verifying it, or grant an AI agent excessive permissions.
So both individuals and companies need to keep the following basic principles in mind.
Check before entering sensitive information into AI
Review code generated by AI instead of running it immediately
Give AI services only the minimum permissions they need
Check the data-handling policy of external AI services
Have a person verify important tasks carried out by AI
Even these basic habits alone can help reduce some of the risks that can arise while using AI.
Conclusion
CSK 2026's "The AX Era: What National AI Security Strategy Is Needed?" session is meaningful in that it looked at the development of AI technology not simply as a new industry opportunity, but together with the cybersecurity environment that's changing alongside it.
AI can become a powerful tool for attackers, and it can become a powerful tool for defenders too.
So the competition going forward is unlikely to stay limited simply to who has the more powerful AI.
Who can develop, use, and control AI more safely is also likely to be an important factor.
Topics discussed at CSK 2026 — a national, shared AI security standard, zero trust, automated defense systems, AI agent security, and technological sovereignty — are areas that will keep mattering as AI becomes more deeply embedded in our lives and industries.
Ultimately, the core task of the AX era isn't about viewing AI adoption and security as opposing goals, but rather
"how do we build an environment where AI can be used safely?"
— that is the perspective it needs to be approached from.
Please refer to the Cyber Summit Korea (CSK) 2026 website (https://cybersummit.kr)