CSK 2026 [Conference] Special Lecture - An Easy Guide to Manufacturing Foundation Model Security and the International Cyber Exercise APEX
The CSK 2026 special lecture examines security challenges arising from the growing use of foundation models in manufacturing, including risks involving data, models, supply chains, and AI operations.
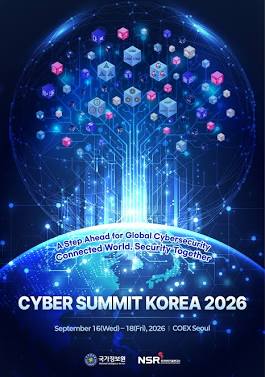
Cyber Summit Korea (CSK) 2026. (Source: CSK 2026 Cyber Summit Korea website)
CSK 2026 Session C-4 Special Lecture
An easy guide to manufacturing foundation model security issues and the international cyber exercise APEX
As artificial intelligence spreads rapidly into manufacturing sites and the cybersecurity field, "how do we use AI safely" is now becoming just as important a task as "how do we use AI."
In manufacturing in particular, information generated in the production process — sensor data, equipment information, product images, quality data, work documents, and recipes — can be used for AI training and analysis.
When this kind of data is combined within a single AI model, it can help improve productivity and quality, but the flip side also needs to be considered: a company's core technology and know-how could end up exposed externally through the AI.
At CYBER SUMMIT KOREA 2026, held in September 2026, a range of programs were arranged to look at both this kind of AI-era security issue and international cyber-defense cooperation together.
This article focuses especially on the Session C-4 special lecture and organizes, in an easy-to-follow way, its two topics —
"Security Issues and Responses for Manufacturing Foundation Models" — Professor Ko Young-myung (POSTECH)
and "An Easy Guide to the International Cyber Exercise APEX" — CEO Kim Han-soo (SegFault; YouTuber 'Normaltic')
.
1. What kind of event is CSK 2026?
CYBER SUMMIT KOREA 2026, or CSK 2026 for short, is a cybersecurity event centered on global cybersecurity that brings together experts, institutions, companies, and academia from Korea and abroad.
The 2026 event was held at COEX Seoul from September 16 to 18, hosted by the National Intelligence Service and the National Security Research Institute.
CSK 2026 broadly ran the following programs.
The cybersecurity conference
The international cyber exercise, APEX
The Cyber Conflict Exercise, CCE
Exhibition/promotional booths
The Youth White Hat Hacker Academy
A university student paper presentation session, and more
One characteristic of this event is that AI has fully emerged as an important topic in cybersecurity.
The relationship between AI and security was discussed across a range of fields, including high-performance AI threats, AI security strategy, international cyber cooperation, and cyber training.
In other words, it's become an era where, alongside using AI to innovate work and industry, we also need to respond to new attacks that use AI and to security issues within AI systems themselves.
2. What did the Session C-4 special lecture cover?
The Session C-4 special lecture covered two different topics: AI security in manufacturing, and international cyber training.
The first presentation's topic was
"Security Issues and Responses for Manufacturing Foundation Models."
The second presentation was on the topic of
"An Easy Guide to the International Cyber Exercise APEX."
The session was chaired by Director Park Ki-tae (National Security Research Institute).
Looking at both presentations together reveals a shared thread.
That is, AI and cybersecurity are no longer the problem of a single technology, but are expanding into a security issue at the level of industry and the nation.
3. What is a manufacturing foundation model?
Let's first understand the manufacturing foundation model (MFM).
A foundation model refers to an AI model built by training on a large amount of varied data so it can be applied to multiple tasks.
The generative AI we typically use, for example, is trained on various data like text and images so it can carry out multiple kinds of tasks.
This kind of AI model can be used in manufacturing too.
For example, the following kinds of data are generated on a manufacturing floor.
Equipment sensor data
Production process data
Product images
Quality inspection data
Work documents
Production recipes
Material and physical-property data
Equipment operation data
Workers' experience and know-how
If AI can comprehensively understand this kind of data, it can support various problems on the manufacturing floor.
For example, the following uses become possible.
Process optimization
Data generated during production can be analyzed and used to improve process conditions.
Quality inspection
AI can analyze product photos or inspection data to determine whether a product is defective.
Predictive maintenance
Sensor data from equipment can be analyzed to identify the possibility of a failure in advance.
Improving productivity
Various production data can be analyzed comprehensively to find inefficiencies in the production process.
In this way, manufacturing AI can go beyond simply answering questions and connect directly to decision-making and the production process on the factory floor.
4. So why does security matter for manufacturing AI?
One important characteristic that sets manufacturing AI apart from general AI is that the training data itself can be a company's core asset.
For example, suppose a company has a manufacturing recipe it uses to produce a particular product.
That recipe can include information like the following.
The type of raw material
The mixing ratio of raw materials
Process temperature
Pressure
Time
Equipment conditions
Production sequence
Quality-control standards
This kind of information isn't simple data — it can be manufacturing know-how a company has accumulated over a long time.
Also, analyzing equipment data over a long period can produce information that reveals a specific factory's equipment configuration or production characteristics.
So in the process of training a large-scale AI model on manufacturing data, the following question is necessary.
"Is the AI learning the data well?"
and beyond that,
"Is the data the AI learned being kept safe?"
— this question needs to be asked together with the first.
5. Major threats to think about with manufacturing foundation models
This presentation covers several security threats that can arise with manufacturing foundation models.
Representative examples include data extraction, model inversion, gradient leakage, and poisoning.
Let's look at each one in an easy way.
5-1. Data extraction
This is an attack that tries to infer sensitive information included in the training data by repeatedly querying an AI model or analyzing its outputs.
For example, if manufacturing AI repeatedly gives overly specific answers to questions about a particular production process, an attacker could combine those answers to estimate a company's manufacturing information.
This is why an AI model's answers themselves need to be managed from a security standpoint.
5-2. Model inversion
This is an attack that analyzes a model's behavior or output to work backward and estimate characteristics of the data used to train it.
If manufacturing AI has been trained extensively on data from a particular piece of equipment or product, it may be possible to analyze the model's output to try to estimate features that were present in the original data.
In other words,
data → AI model
isn't the only flow that matters — the reverse risk of
AI model → estimating characteristics of the training data
needs to be considered too.
6. What is gradient leakage?
When training an AI model, the model's parameters are updated using the data.
In an environment where the gradient information generated in this process needs to be transmitted externally, the possibility that this information could expose some characteristics of the original training data can become a problem.
This matters especially in environments where multiple organizations take part in training an AI model without directly sharing their data with one another.
In manufacturing, a method that avoids sending the data itself outside may be preferred, but that doesn't automatically make all information safe.
The information transmitted during the model-update process needs to be treated as something to secure too.
7. What is a poisoning attack?
Poisoning is an attack that intentionally corrupts the data an AI trains on.
For example, if an attacker mixes incorrect data into the training process where normal manufacturing data should be used, it can affect the AI's judgment.
This kind of problem can matter even more in manufacturing AI.
If AI is used to judge production quality or equipment condition, incorrect training data can lead directly to a mistaken judgment by the AI.
So for manufacturing AI,
how much data has been gathered
isn't the only question —
whether that data can be trusted
needs to be checked too.
8. Manufacturing AI security is hard to solve with a single technology alone
Protecting a manufacturing foundation model requires an approach that combines multiple defensive measures together, rather than applying just one security technology.
The main response directions raised in the presentation can be summarized simply as follows.
Differential privacy
This is a technology that reduces, in a defined way, the influence of personal or sensitive data so it isn't exposed as-is.
It can be used to reduce how much a specific piece of data stands out in an AI's training results.
Federated learning
Rather than gathering all data in one place, each institution or company trains its own model and only shares the necessary information.
This has potential in situations where manufacturing companies find it difficult to share data with one another directly.
That said, federated learning also needs to account for the possibility of information leaking through things like model-update information.
Machine unlearning
This is a technology for removing a specific piece of data's influence from a model after the AI has already trained on it.
It's an important research area for situations involving a data-deletion request or the need to remove a specific piece of data's influence.
Access control
This is about managing who can access which AI models and data.
Not every employee or system needs access to all manufacturing data.
It's important to divide permissions so access is limited to what's needed for the task at hand.
MLSecOps
This is an approach that applies security together throughout the machine-learning development and operations process.
Rather than developing an AI model and adding security at the very end,
it means building security into the entire process — data collection → training → model validation → deployment → operation → monitoring
.
9. Governance matters for manufacturing AI too
There's a reason AI security can't be solved by technology alone.
It's because manufacturing data can include a company's core technology and know-how.
So organization-level standards are needed for questions like the following.
What data will be used to train the AI?
Where will sensitive manufacturing data be stored?
Who can access the data?
Is it acceptable to enter data into an external AI service?
Does a person need to verify the results AI generates?
Who will approve model updates?
Who is responsible when a problem occurs?
Managing these kinds of questions comprehensively is what AI governance means.
This matters especially when core national technology or a company's core manufacturing technology is involved — alongside technical security, a protection system on the institutional and policy side becomes important too.
10. The second presentation: what is the international cyber exercise APEX?
The second presentation's topic was
"An Easy Guide to the International Cyber Exercise APEX."
APEX stands for Allied Power Exercise, an international cyber exercise meant to strengthen international cybersecurity cooperation and solidarity.
According to official CSK materials, APEX began in 2024 and uses cyber-warfare scenarios based on a hypothetical inter-state conflict situation.
Participating countries take part as defense teams (Blue Teams) responding to cyberattack scenarios.
Put simply,
"an exercise where multiple countries assume that a real cross-border cyber crisis has occurred and work together to defend against cyberattacks"
— that's how it can be understood.
11. Why is APEX necessary?
Cyberattacks have no borders.
No matter what country an attacker is in, they can attack a company or institution in another country over the internet.
A single attack can also affect multiple countries and institutions at the same time.
So there's a limit to how much a single country can block every attack on its own.
In an actual cyber crisis, cooperation like the following can become necessary.
Sharing attack information
Threat analysis
Assessing the scope of a breach
Blocking the spread of an attack
Discussing response methods
Recovery support
Post-incident analysis
International exercises like APEX serve to let participants practice this kind of cooperation process in a situation resembling the real thing.
12. What kind of training happens in APEX?
APEX isn't simple classroom-style theory education.
It creates a hypothetical cyber crisis and has participants respond the way a real defense team would.
For example, suppose a cyberattack occurs in a hypothetical country.
The defense team would then carry out a process like the following.
① Checking the attack situation
Checking whether anomalies have occurred in the system.
② Threat analysis
Analyzing what type of attack it is.
③ Assessing the scope of damage
Checking which systems or networks were affected.
④ Deciding on a response method
Deciding what measures to take to prevent further damage.
⑤ International cooperation
Sharing necessary information with other participating countries or institutions.
⑥ Responding to the attack
Responding to the attack and blocking further compromise.
⑦ Post-incident analysis
After the exercise ends, analyzing which responses were effective and what needs to be improved.
In other words, the core of APEX isn't just testing "technology for blocking attacks" — it can be seen as checking the ability of nations and institutions to cooperate with one another.
13. What stands out in APEX 2026: the AI defense team
What's especially notable about APEX 2026 is that an AI-driven Blue Team was newly formed.
As the potential for AI to be used in cyberattacks grows, the need to use AI in defense is growing too.
Where the traditional approach centered on people checking and analyzing security events before deciding how to respond, using AI can develop this into quickly analyzing large volumes of security data and finding anomalies.
Furthermore, AI can automate part of the response process too, beyond just detection and analysis.
But AI defense brings new challenges as well.
If AI makes a wrong judgment, it can actually create problems for the security response.
So for an AI defense team,
using AI isn't the goal in itself — what matters is verifying how reliably AI can make judgments in an actual cyber-threat situation
.
14. Competition between AI attack and AI defense
In the AI era, both attackers and defenders can use AI.
Attackers might use AI to gather attack information, find vulnerabilities, or automate the attack process.
Conversely, defenders can use AI to analyze large volumes of security data, detect anomalous behavior, or support the response process.
In this kind of situation, the speed of cybersecurity matters too.
That's because an attack can progress while a person is still analyzing every event one by one.
So going forward,
a structure combining people + AI
to carry out security is likely to become even more important.
That said, important judgments shouldn't be handed over to AI unconditionally — a system for verifying and controlling AI's output needs to be built alongside it.
15. How are manufacturing AI security and APEX connected?
On the surface,
"manufacturing foundation model security"
and
"the international cyber exercise APEX"
look like different topics.
But they share a common core.
That is, as AI enters more real-world environments, security needs to be designed together with AI as well.
On a manufacturing floor, AI analyzes production data.
In national cyber defense, AI can analyze cyber threats.
In the end, both fields share the same flow —
data → AI → judgment → real-world action
.
So it's necessary to prepare in advance for what happens when AI's judgment is wrong, how to respond if the data gets corrupted, and who should be able to access the AI.
16. Basic principles of AI security that will matter going forward
Whether it's manufacturing AI or cyber-defense AI, the following basic principles apply.
First, provide important data on a minimal basis
Just because AI needs data doesn't mean every piece of data has to be provided unconditionally.
Provide only the data needed for the task, and protect sensitive information separately.
Second, don't blindly trust AI's output
No matter how sophisticated AI is, errors can occur.
Important decisions need a human review and approval process.
Third, manage AI access permissions
Not everyone should be able to access AI models and sensitive data.
Permissions need to be divided by user and by system.
Fourth, check the source and quality of training data
AI's performance is heavily influenced by its training data.
So it's necessary to check where the data came from, whether it's been tampered with, and whether it can be trusted.
Fifth, continuously monitor AI systems
AI isn't a system that's finished once it's developed.
Because new attacks or errors can occur during operation, continuous checking is necessary.
17. Conclusion
The two topics covered in CSK 2026's Session C-4 special lecture may look like different fields, but they can be understood as connected by a single throughline: cybersecurity in the AI era.
"Security Issues and Responses for Manufacturing Foundation Models" shows that as AI makes broader use of data and knowledge from the manufacturing floor, how to protect a company's core data and manufacturing know-how becomes an important issue.
"An Easy Guide to the International Cyber Exercise APEX," meanwhile, helps explain why, in order to respond to cross-border cyber threats, training where multiple countries and institutions respond together in a situation resembling reality is necessary.
In particular, the fact that an AI defense team newly took part in APEX 2026 is a case showing the potential for AI to play an important role going forward not just as an attack tool, but as a defensive one too, in cybersecurity.
In the end, security in the AI era doesn't simply mean technology for blocking hacking.
protecting data, protecting AI models, verifying AI's judgments, having people control AI, and, where necessary, building a system where nations and institutions can respond together — this is what matters.
As AI use expands across manufacturing, national cyber defense, and a range of other fields going forward, AI security is likely to become not an optional feature, but a basic condition for using AI safely.
This CSK 2026 special lecture was a topic that prompts reflection, amid this shift, on the fact that how safely AI is used is becoming just as important as how cleverly it's used.
Please refer to the Cyber Summit Korea (CSK) 2026 website (https://cybersummit.kr)